Each KeyCom user is identified based on their personal unique username.
Creating new users
On the Admin site, go to the Authentication and authorization -> Users group and click ADD USER.
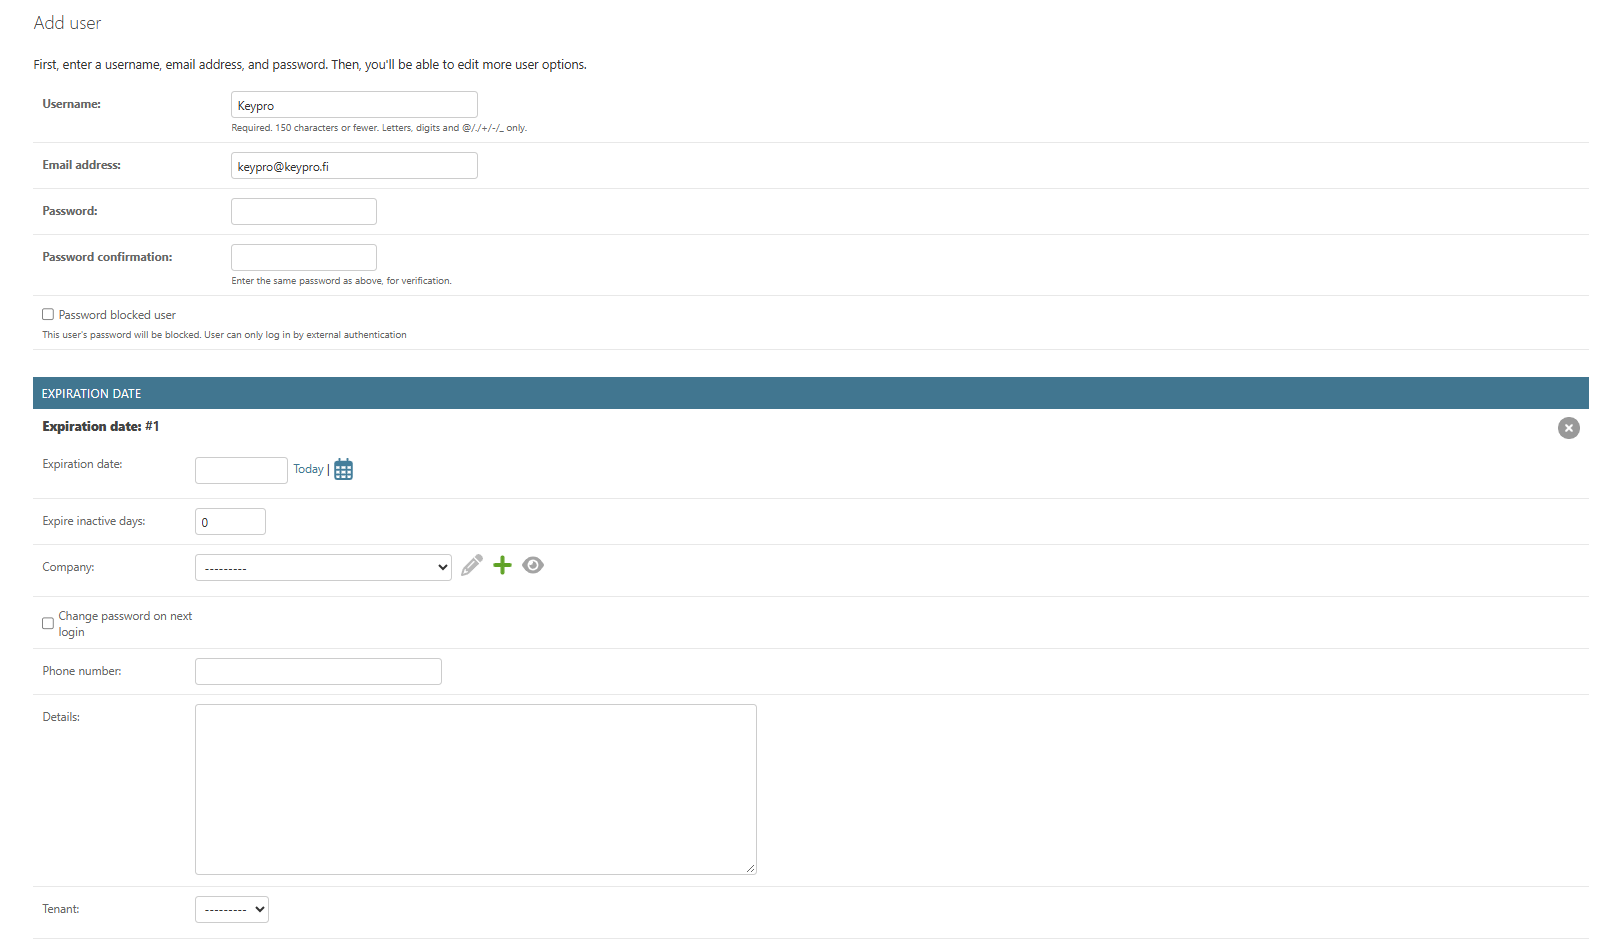
- Complete the Username, Email and Password fields.
- Define an Expiration date if you want to limit the validity of the username.
- Click Save.
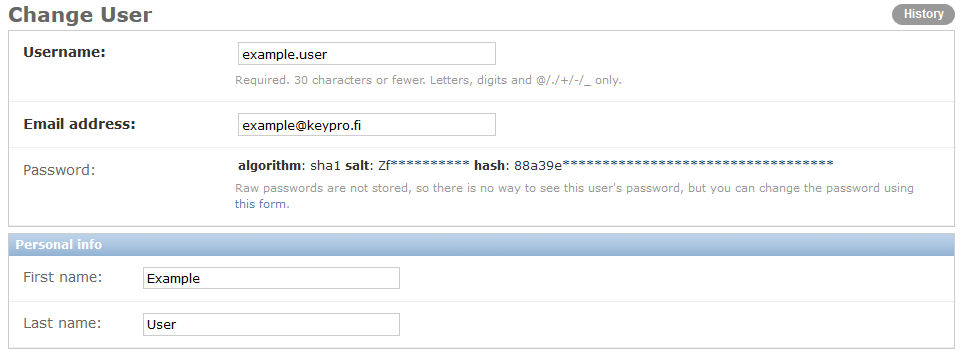
- On the displayed form, enter the first and last name of the user:
- Define the access rights for the user as instructed in the Defining and modifying access rights for usernames chapter starting from step 2.
Defining and modifying access rights for usernames
Selecting user groups for the user:
- Select the username on the Users list.
- On the Available groups list, select the user groups to which the user belongs.
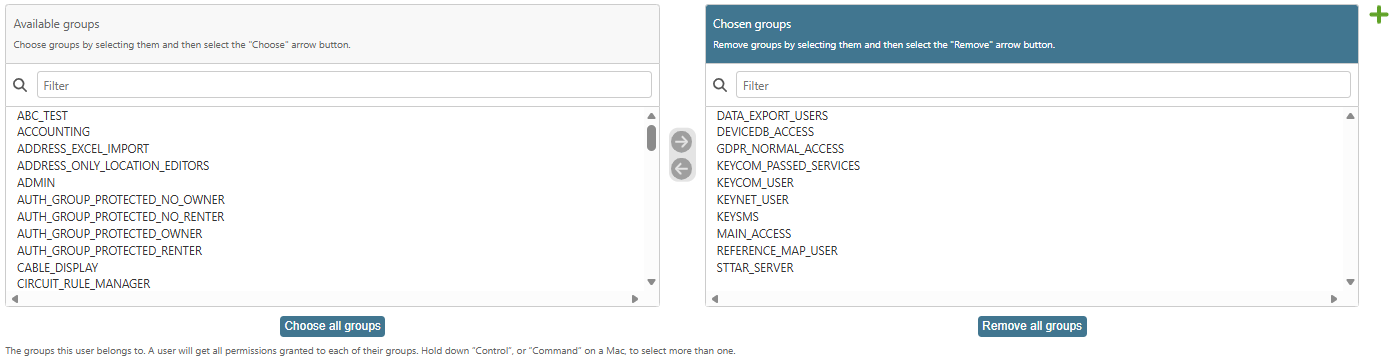
- Click the arrow button displayed between the lists to add groups to the Chosen groups list.
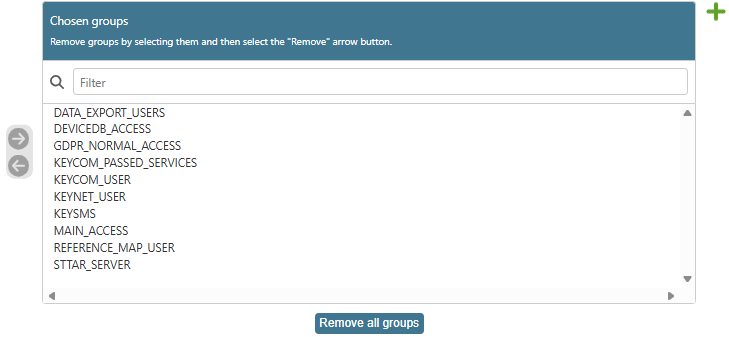
- You can define user-specific permissions in a similar manner.
- Save changes.
Available user groups in KeyCom
The following user groups have been defined as default groups in KeyCom:
- KEYCOM_USER is a user authorized to add, modify and delete network objects.
- KEYNET_USER is a user authorized to use the KeyNet functions.
- KEYCOM_VIEWER is a user authorized to view network objects.
- KEYNET_VIEWER is a user authorized to view KeyNet data.
- DEVICEDB_ACCESS is a user authorized to use the device database forms that can be opened from the telecom premises form.
- CABLE_DISPLAY is a user authorized to view maps, duct route objects and cable objects.
- DATA_EXPORT_USERS is a user authorized to export data to another data format by using the export function.
- POWER_USERS is a group that will be removed. Use the KEYCOM_USER and KEYNET_USER groups instead.
- PREM_ADMIN is a user authorized to modify restricted telecom premises on Telecom premises form.
- DEVICE_GROUP_ADMIN_USER is a user authorized to create, edit, and delete device groups.
- READONLY_USERS_PLUS_ANNOTATION is a user with viewing rights and the right to create annotations.
- READONLY_USERS_PLUS_AREA is a user with viewing rights and the right to create areas.
- REFERENCE_MAP_USER is a user authorized to import files to the map by using the spatial upload function.
- ACCOUNTING is a user authorized to access the log-in data of users.
- MASS_DELETE is a user authorized to delete several objects at once. The mass deletion function of the application must be activated for this.
- MAIN_ACCESS is a user authorised to use the main application only. KEYCORE_IGNORE_MAIN_VIEW_ACCESS_GROUPS must not be in an active state in the application.
- VIEWER_ACCESS is a user only authorized to use KeyMobile. KEYCORE_IGNORE_MAIN_VIEW_ACCESS_GROUPS must not be in an active state in the application.
- KPI_REPORT is a user authorized to run KPI reports. (A customer-specific feature)
- GDPR_NORMAL_ACCESS is a user authorized to view customer data.
- GDPR_EXTENDED_ACCESS is a user authorized to view customer data and customer data of the “Private–restricted” type (see Customer types).
- OM_CIRCUIT_ADMIN allows updating of circuit sections and its related components when the usage state of the circuit section is in O&M (operations and maintenance) state. The KN_USAGE_STATE Numeric value 4 field tells if the circuit section usage state is in O&M state. Value of 1 means that the state is in O&M state. The OM_CIRCUIT_ADMIN group only allows the user to edit/delete circuits in O&M state on Circuit form and allows the user to use the Logical Mass Connection Change functionality. The group has no effect on other forms.
- DIARY_VIEW is a user authorized to view Diary feature related functionalities.
- DIARY_EDIT is a user authorized to view, create and edit Diary feature related functionalities.
- DIARY_FULL is a user authorized to view, create, edit and delete Diary feature related functionalities
- UV_USER is a user who has viewing access and limited modifying access to KeyWork forms. This user group always must be active if there’s also additional UV user groups that need to be active in the environment.
- UV_CONTRACTOR_DIRECTOR is a user who has director’s rights. They have the rights to control and supervise the work related to the contractor.
- UV_CONTRACTOR_MECHANIC is a user who has mechanic’s rights. They have the rights to carry out tasks related to the UV contractor.
- UV_MAINTENANCE_CONSTRUCTOR is a user who only has access to KeyWork forms but no editing rights.
Ficora reporting rights
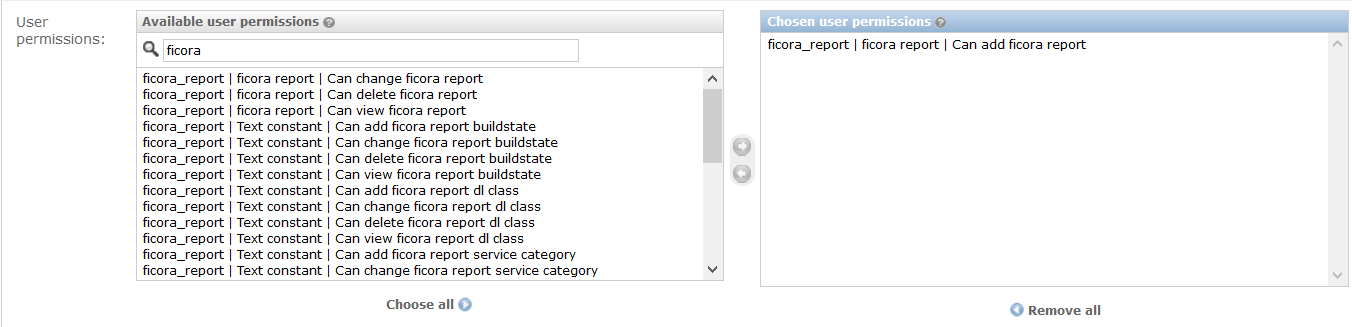
Users with Can add Ficora report added to the Chosen user permissions field have Ficora reporting rights.
Two phased authentication for a user (optional)
If two-factor authentication has been ordered as an additional service, the user page includes fields that control how the user receives the confirmation code. The fields are in the section titled Expiration date.
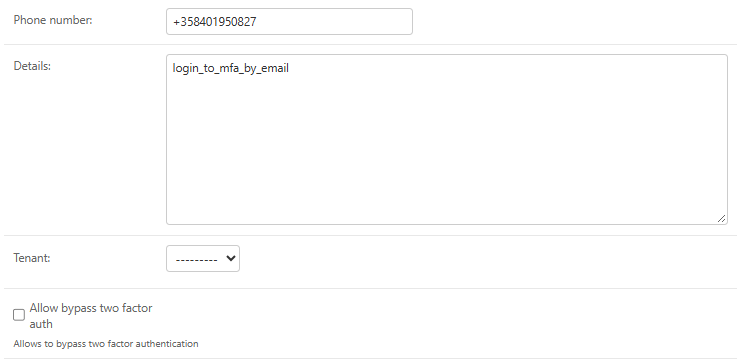
The confirmation code is sent to the user either by email or by SMS:
- Email: The code is sent to the user’s email address when the Details field contains login_to_mfa_by_email.
- SMS: The code is sent by SMS to the number in the Phone number field. If the phone number is missing code is sent to the user via email.
Note! If the user has neither a phone number nor an email address, the code cannot be sent. The login then fails with the message No contact details for verification. Contact your administrator.
Define two-factor authentication for a user
- Select the username on the Users list.
- Choose how the user receives the confirmation code:
- By SMS: Enter the user’s phone number in the Phone number field, including the country code (for example +358401234567).
- By email: Make sure the user has an email address, and enter login_to_mfa_by_email in the Details field.
- Make sure Allow bypass two factor auth is cleared. Select it only if the user is allowed to log in without two-factor authentication.
- Save changes.
Deleting usernames
To delete an existing username, select the username on the Users list and click Delete on the displayed form.
Changing user passwords
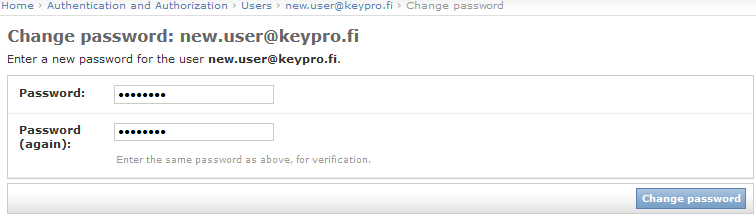
Users can change their own passwords through the link in the applications main view. Admins can change the passwords of a user on the Change User form by clicking the “this form” link.
For security reasons, passwords are stored in the system database with strong encryption, and not even admin users can view the passwords of users through the admin interface.
Sharing map views
In KeyCom, you can share a predefined map view with specific users. This map view will be set as their default view from their first login.
To share a map view for an existing user, do the following:
- Select a user from the list by enabling the check box next to their username.
- Select Add shared map view from the Action menu and select Go.

- In the page that open, paste the map link link to the Shared Map View Link field. (You can obtain the link from the Map views form and by clicking Copy map link to clipboard
 ).

- Click Fetch link name and default to automatically fill in the Name field and set the map view as the default.
To edit the name, simply edit the text in the Name field.

Finally, click Save to set the map view for the selected users.